Your SPRS score. Your signature. Backed by evidence.
NIST SP 800-171 and CMMC self-assessment for small and mid-size defense contractors. Assess every objective, score it under the DoD methodology, fix the gaps, and sign your annual affirmation with the record in front of you.
Certification paused. Your signature didn't.
DoD suspended CMMC Phase 2 third-party certification in July 2026. The obligations under DFARS 252.204-7012 did not change: implement all 110 NIST SP 800-171 requirements, post your self-assessment score in SPRS, and have a senior official affirm compliance every year. Without an outside assessor, the company that signs has to be able to prove its score.
Assess. Score. Remediate. Affirm.
One workflow that mirrors the obligation, with every change recorded on an immutable audit trail.
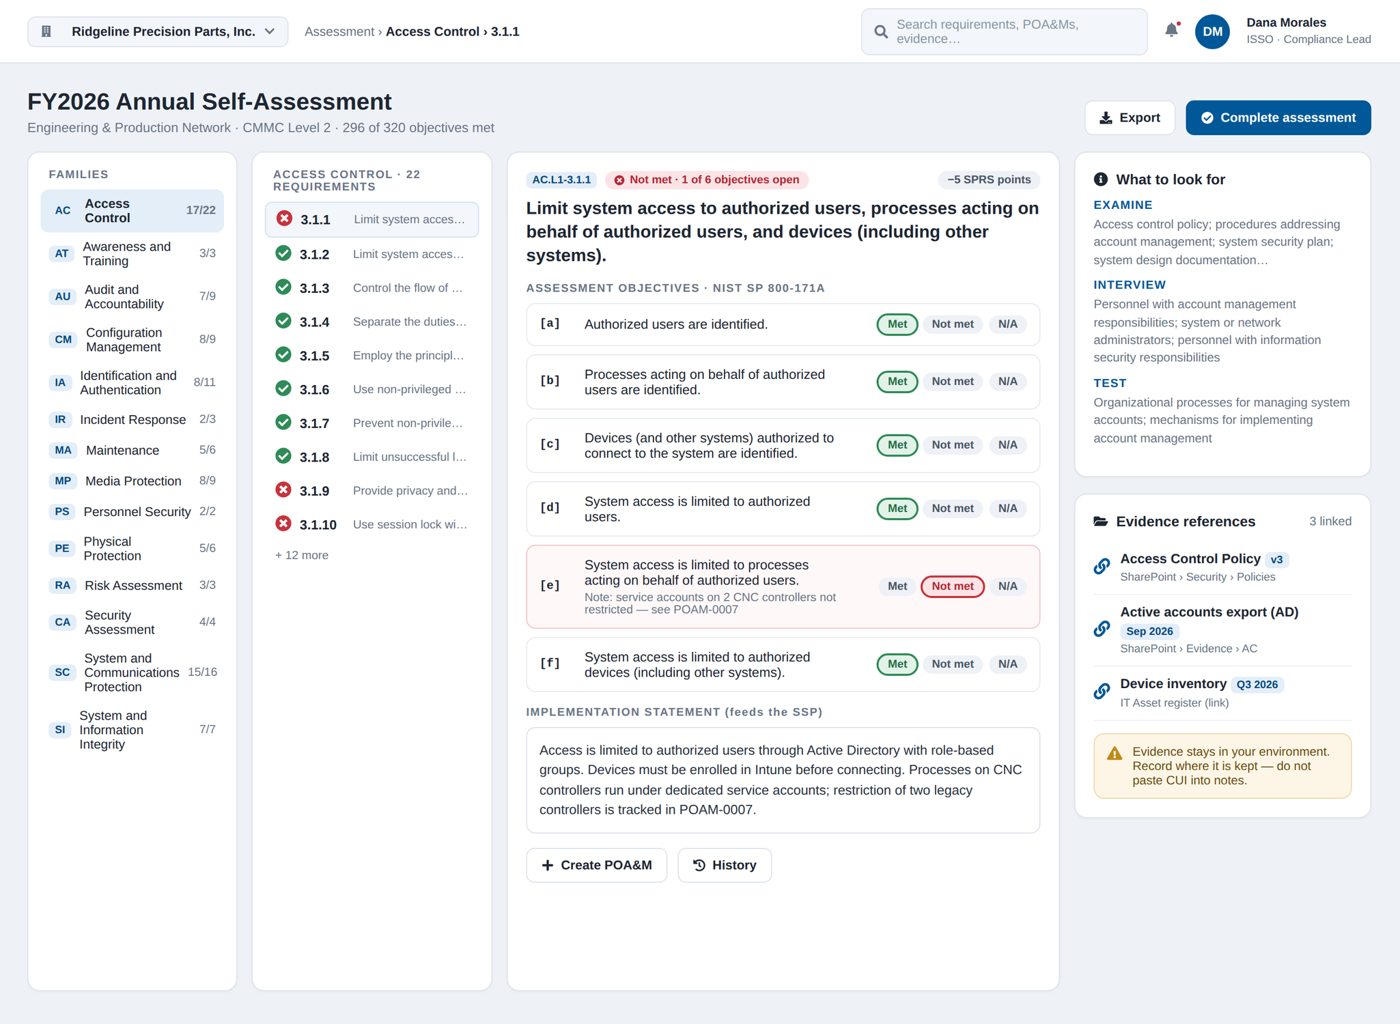
Assess every objective
Test all 320 SP 800-171A objectives in NIST's own wording, not just the 110 headline requirements.
- Examine, interview and test guidance beside each requirement
- A requirement is met only when every objective is met
- Implementation statements flow straight into your SSP
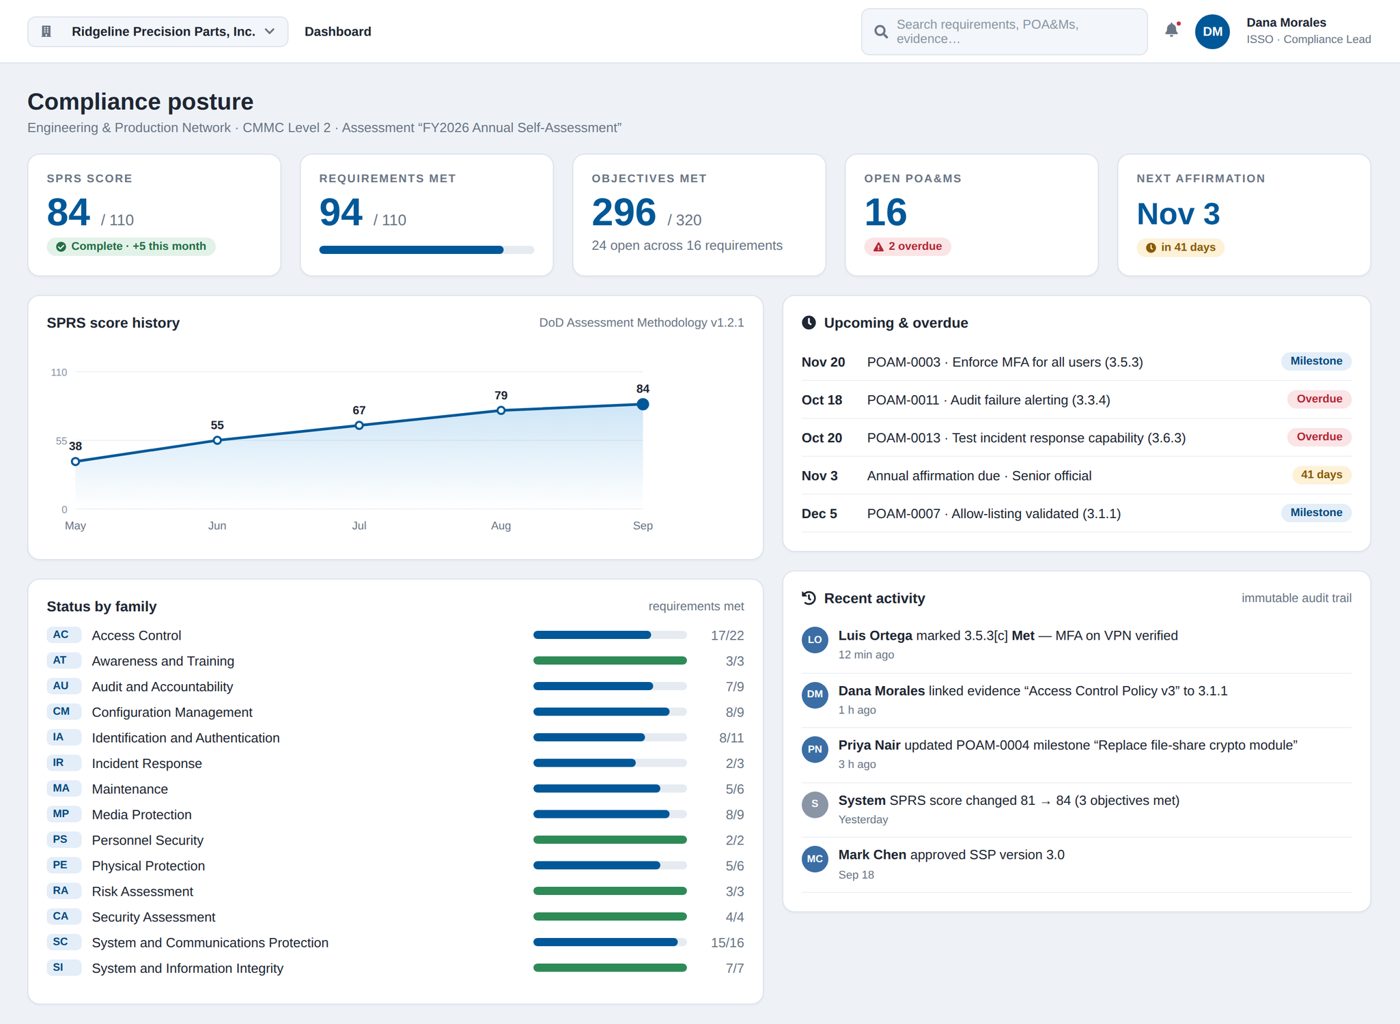
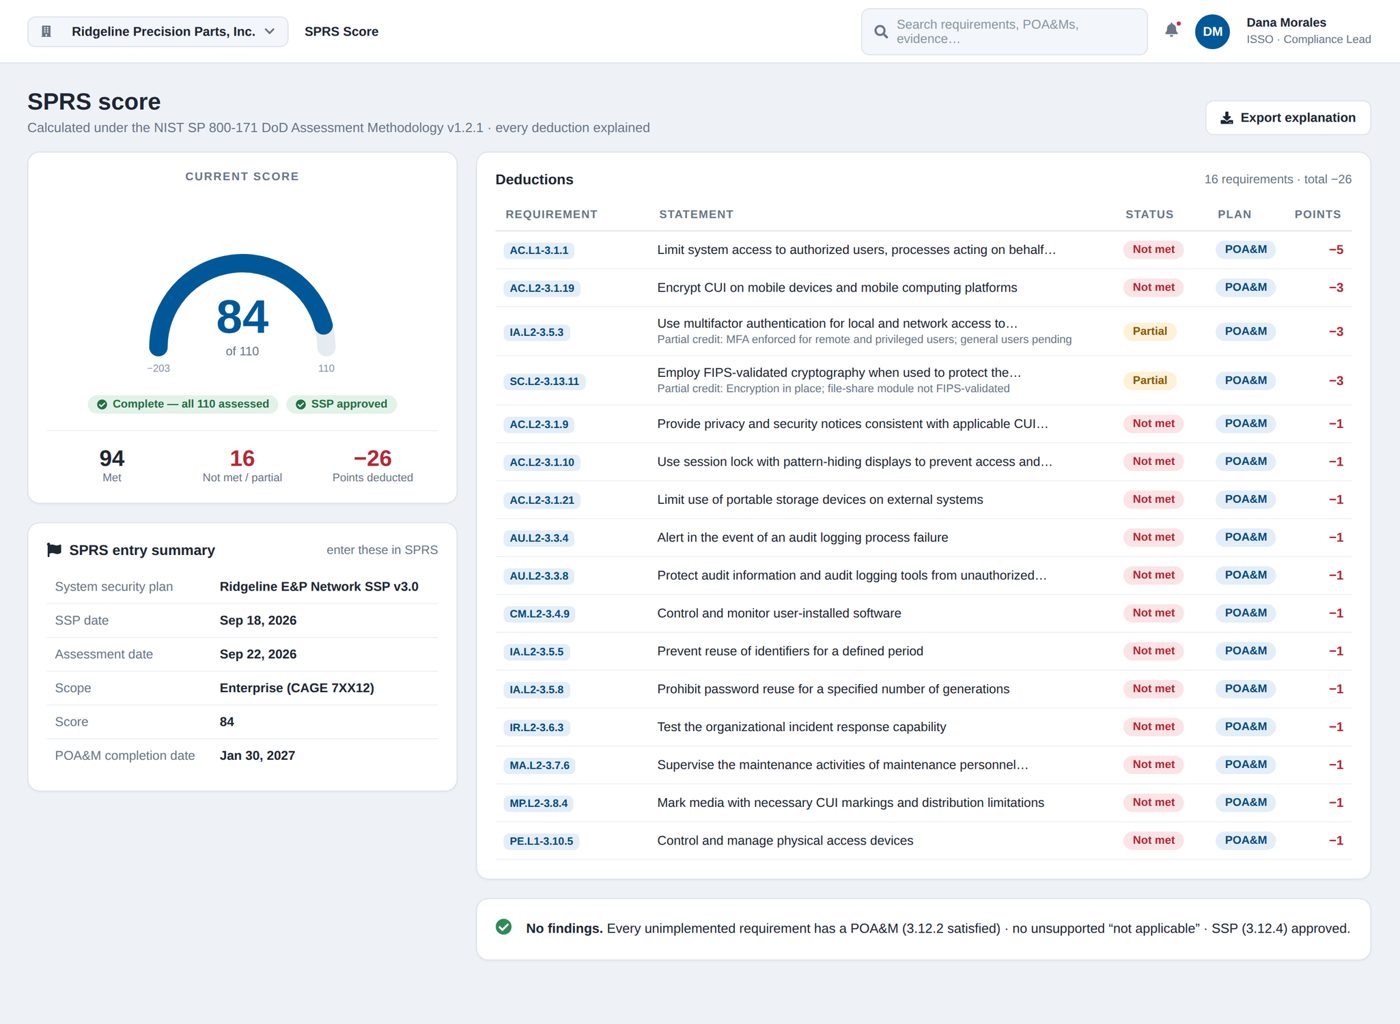
A live SPRS score that explains itself
Calculated under the DoD Assessment Methodology, recalculated the moment an objective changes.
- Every deduction linked to the objective behind it
- Partial credit handled the way the methodology allows
- No SSP, no score; unsupported "not applicable" is flagged
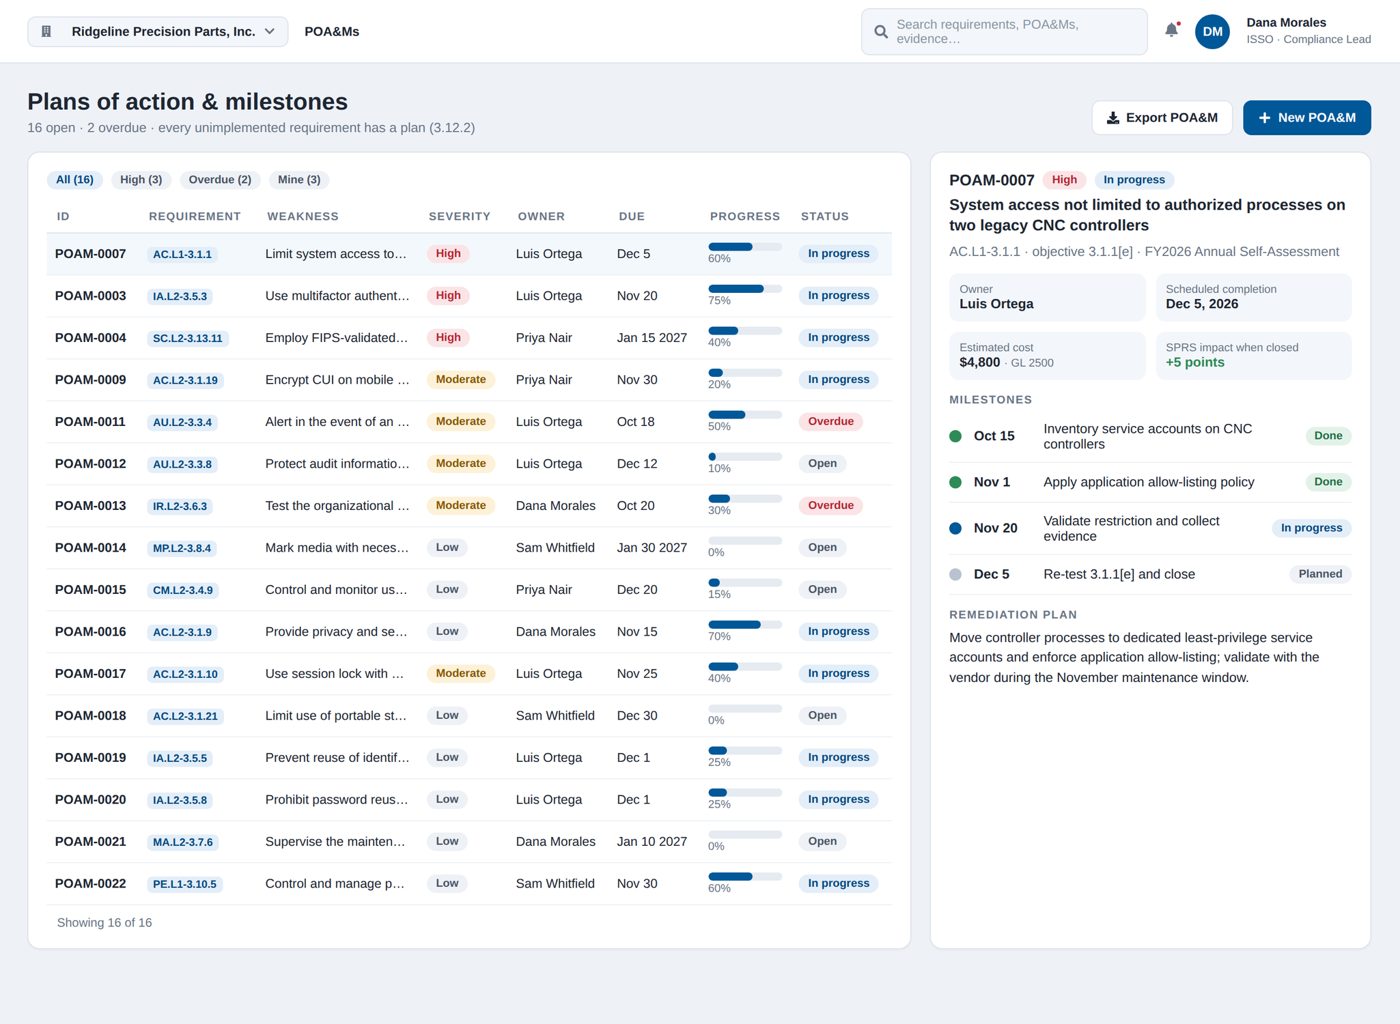
Every gap gets a plan, an owner and a date
POA&Ms are created from not-met results and tied to the requirement they fix.
- Owners, milestones and reminders before dates slip
- Remediation cost tied to the controls it fixes
- Warns when an open requirement has no plan
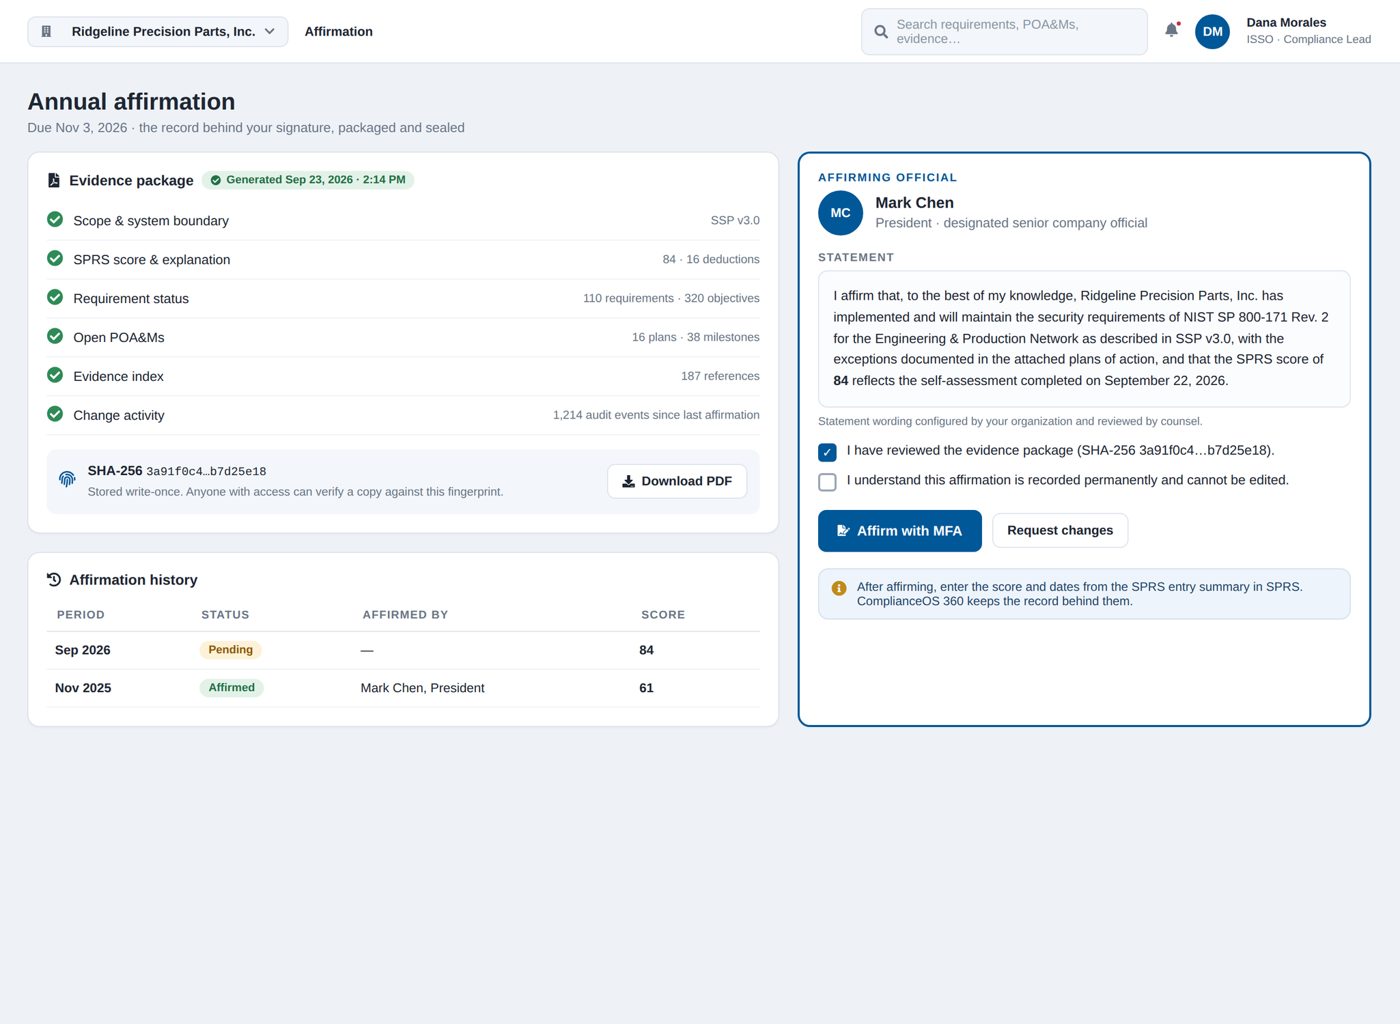
Sign with the record in front of you
Your SSP and a tamper-evident evidence package are generated from the same record as your score.
- Score, status, open POA&Ms and evidence index in one package
- Hashed and write-once, so it can't be edited after the fact
- The exact values to enter in SPRS
Product screens shown with an illustrative company and data.
Held to the standard we help you meet
No CUI in the platform
ComplianceOS stores assessment status and evidence references, not your files. Your evidence stays in your own systems.
Separated by customer
Each customer's data is isolated in the application and enforced by the database.
MFA and least privilege
Multi-factor sign-in for administrators and role-based access for everyone else.
Immutable audit trail
Every change is recorded automatically. No one can edit or delete the history.
U.S. hosting
Hosted on AWS in U.S. regions. Data, backups and logs stay in the United States.
Encrypted throughout
TLS in transit and managed-key encryption at rest.
Plans
Priced for small contractors, per company, with annual and monthly billing. Contact us for pricing.
Essentials
Contractors with up to 25 employees · up to 5 users
- All 110 requirements and 320 objectives
- Live SPRS score under the DoD methodology
- POA&Ms, generated SSP and affirmation package
- Immutable audit trail
Professional
Contractors with 26 to 500 employees · unlimited users
- Everything in Essentials
- Remediation cost visibility
- Full evidence package and score history
- Guided onboarding
Higher Education Add-On
For colleges and universities · added to Professional · in development, ask about early access
- GLBA Safeguards Rule, NIST CSF 2.0 and Texas Cybersecurity Framework
- Annual GLBA report to your board
- Qualified Individual and risk assessment records
- Campus and department roles, single sign-on
- No student records stored
Need help getting ready? Oakward Solutions also offers readiness assessments, remediation support and managed compliance. Ask about a bundle.
Request a demo or join the pilot
See ComplianceOS 365 with sample data, or start a 30-day pilot in your own workspace with guided onboarding. Pilot workspaces do not accept CUI.
We reply within one business day.